AI adoption has exploded in recent years with the Federal Reserve estimating that 78% of the labor force works at firms that have adopted AI. While some people have differing opinions on this, there is one aspect that we should have a consensus. While opinions on AI differ, there is one aspect businesses should agree on: the importance of choosing a secure AI platform over an insecure one.
AI does have the power to provide major productivity benefits, but not every AI platform handles business data the same way. So, executives should be asking this question: Does the AI provider we use train their model on our company data?
This is what we’ll dive into and discuss the difference in AI security and how companies can choose a secure AI platform over an insecure AI platform.
Enterprise AI Security: What Is Secure AI?
From a business perspective, we can define secure AI as an AI system that is intentionally designed, configured, and governed to reduce business risk. That includes protecting sensitive data, controlling who can access the system, preventing unauthorized or inappropriate use, maintaining compliance, monitoring how AI is being used, and ensuring the organization retains oversight of its AI tools and outputs.
A secure AI platform should also include safeguards such as:
- Access controls
- Encryption
- Data retention policies
- Administrative controls
- Audit capabilities
- Vendor transparency
An AI tool such as a large-language model (LLM) being popular doesn’t automatically mean it’s appropriate for company data. Safeguards should be put in place to ensure that any data entered into these tools is not stored and used to train the model itself. AI security affects the entire business, not just the department using it.
What Makes AI Insecure for Businesses?
The opposite of secure AI would of course be insecure AI. We would define insecure AI as any environment that creates unnecessary business risk because the organization lacks adequate control, visibility, or protection. Insecure AI doesn’t necessarily mean the AI itself is malicious. Rather, the risk can come from how it collects data, how it’s configured, or how employees use it.
Warning signs can include:
- Data input may be retained or used to improve models
- Unclear policies surrounding usage of company data
- Limited administrative or access controls
- Lack of ability to monitor employee AI usage
- No policies governing what information can be entered
- Weak alignment with the company’s security or compliance requirements
A big concern in the business AI world is the topic of shadow AI. This is the use of unapproved AI tools or applications by employees without the formal approval or oversight of the IT or other departments. A survey from Microsoft found that 78% of AI users are using shadow AI in the workplace. Shadow AI is one of the many ways insecure AI risk can enter an organization.
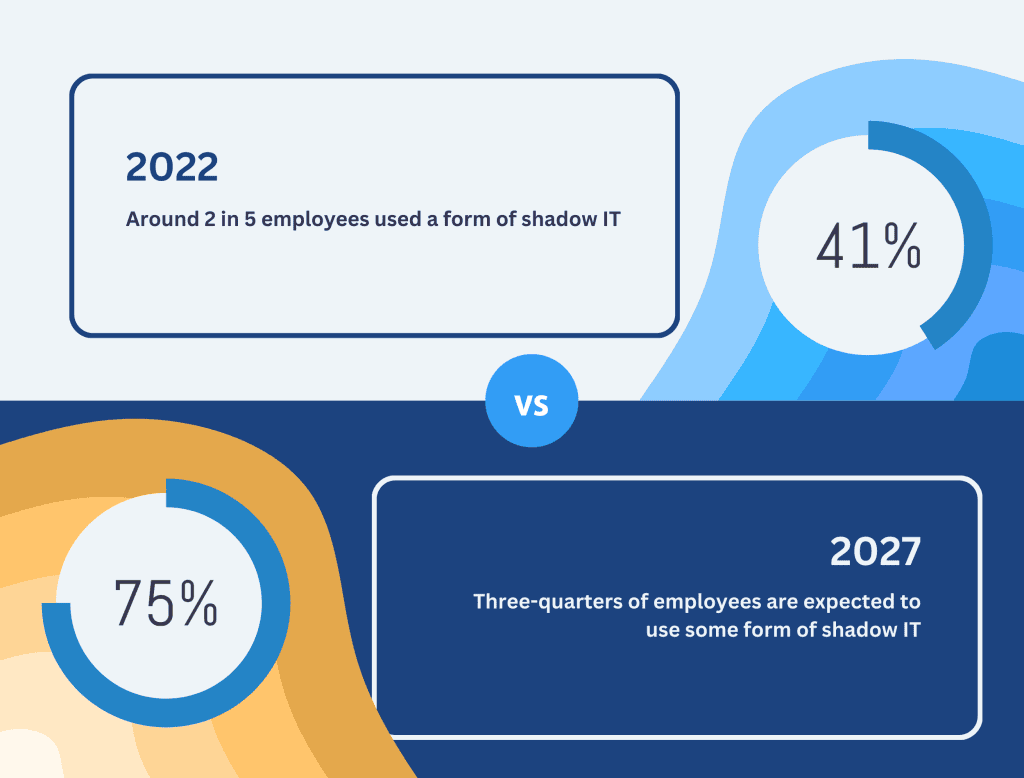
Photo by Programs
Real-World Examples of Insecure AI Use
Insecure AI risks are not hypothetical as we have seen Fortune 100 companies fall victim to this kind of AI risk.
In 2023, Samsung’s semiconductor division allowed engineers to use LLMs. One employee had reportedly pasted source code for semiconductor equipment, while another asked the LLM to generate meeting notes from a confidential internal meeting.
The issue arises when you understand that the employees were sending confidential company data into a third party with no NDA, no data residency controls, and no ability to delete any data entered. Samsung responded by banning all unapproved AI tools. They went on to announce their plan to develop an internal AI system with new AI policies and employee training initiatives.
In 2023, Amazon employees were reportedly entering confidential internal information into ChatGPT. Amazon later warned employees against sharing sensitive company information with the tool after discovering ChatGPT outputs that closely resembled existing internal Amazon data.
The Amazon incident is an example of shadow AI, while both the Amazon and Samsung incidents show how insecure AI use can negatively affect an organization. In both cases, employees had limited control or visibility into how sensitive company data was being stored, retained, or handled once it was entered into the AI platform. If an organization cannot confidently determine where its data is stored, how it is used, and what controls are in place to protect it, that AI environment should be considered insecure.
How Companies Can Choose a Secure AI Tool
Businesses do not need to choose between using AI and protecting the organization. They need to choose AI intentionally. Before approving a platform, leadership and IT should understand whether company data is used for model training, how information is stored and retained, what security controls are available, and whether usage can be governed and monitored.
Companies should also establish approved AI tools, create clear usage policies, and train employees on what information should and should not be entered into AI systems. An MSP or MSSP can help evaluate platforms, integrate them securely, and align AI use with existing cybersecurity and compliance requirements.
Secure AI adoption should be approached with the same care businesses already apply to cybersecurity, technology, and governance.